Key Generation
This section proposes a 130-bits secret key to be used in each session (Stallings, 2002; Forouzan, 2007).
Key generation is considered to be a very important algorithm of block cipher, either symmetric or asymmetric block cipher. In symmetric block cipher or private key block cipher, only a single key is used in encryption of plaintext and in ciphertext decryption. If these two keys are different, that is the encryption key and the decryption key, then knowledge of one key is sufficient to derive the other key.
Table 7.1 (Jha and Mandal, 2011) gives 130-bits key (Stallings, 2002; Forouzan, 2007) generation. The plaintext source file is encrypted by different block sizes with 13 times in
TABLE 7.1
Generation of Secret Key
|
Iteration Number |
Formation of 130-Bits Secret Key |
|||
|
Decimal |
Binary |
|||
|
Block Size |
Option |
Block Size |
Option |
|
|
01 |
128 |
1st |
10000000 |
00(A) |
|
02 |
120 |
3rd |
01111000 |
io(c) |
|
03 |
112 |
2nd |
01110000 |
01 (B) |
|
04 |
100 |
2nd |
01100100 |
01 (B) |
|
05 |
64 |
1st |
01000000 |
00(A) |
|
06 |
60 |
4th |
00111100 |
11(D) |
|
07 |
32 |
2nd |
00100000 |
01 (B) |
|
08 |
30 |
3rd |
00011110 |
10(0 |
|
09 |
16 |
4th |
00010000 |
11(D) |
|
10 |
10 |
1st |
00001010 |
00(A) |
|
11 |
8 |
3rd |
00001000 |
10(0 |
|
12 |
4 |
2nd |
00000100 |
01 (B) |
|
13 |
2 |
1st |
00000010 |
00(A) |
a row of execution. For example, the first iteration or the first round is of 128-bits block size and is encrypted by choosing the first option, for the second iteration or for the second round will be of 112-bits block size and so on. In Table 7.1, block sizes are encoded in 8 bits and options are encoded in 2 bits.
So, in each and every iteration or each round, 10-bits encoded code is obtained. Concatenating these 13 codes of 10-bits each generates 130-bits generated secret key to be used in each session for encryption and decryption. The coded 10-bits values are absolutely pseudo-random. Here, from this table, the 130-bits secret key used for each session is as follows:
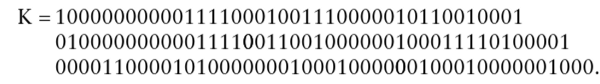
A new secret key will be generated for another new session.
Cryptanalysis
The cryptanalysis finds loopholes in the encryption system and is used to optimize any encryption system. This architecture is mainly based on the RCC, SPN and CBC block of encryption. So this security module has been implemented whereby first 128-bits plaintext is fed to the RCC and then to the SPN. Finally, multiple blocks are encrypted using the CBC mode of encryption.
In this section, a Chi-Square test used for cryptanalysis is used to test the NULL hypothesis. This test measures the difference between plaintext and ciphertext.
The Pearson's Chi-Square test was used (Chakraborty and Mandal, 2006, 2011). This is also known as the Chi-Square goodness-of-fit test or the test for independence or nonhomogeneity or heterogeneity between source file and target file.

where
О is the Observed Frequency ciphertext.
E is the Expected Frequency plaintext, from where О is taken.
df is the "degree of freedom" (n - 1) contains variation of characters.
X2 is Chi-Square calculated using Equation 7.1.
The Chi-Square test is calculated by choosing ten different files which are encrypted with RCC first, then with RSA and finally with TDES, respectively. The program using Equation 7.1 finds the Chi-Square values of these ten files.
Table 7.2 gives the Chi-Square values. Figure 7.5 shows a graphical chart calculated using logarithm base ten scales converted to obtain the Chi-Square value of ten different source files. Observing Table 7.2 and Figure 7.5, we can conclude that the Chi-Square values generated for the proposed cipher, RCC, are greater than those of the RSA encrypted source files, but for TDES, the RCC result is 50% better.
TABLE 7.2
Cryptanalysis of Proposed Micro-Architecture (PMA)
|
File Name |
Size in кВ |
Chi-Square Values |
||
|
PMA |
RSA |
TDES |
||
|
Version.txt |
1 |
1.76 |
1.74 |
1.79 |
|
Ukraine.txt |
5 |
4.95 |
4.88 |
5.08 |
|
Content.txt |
10 |
5.68 |
5.66 |
5.66 |
|
Removdrv.txt |
21 |
5.83 |
5.82 |
5.90 |
|
PropList.txt |
53 |
5.81 |
5.80 |
5.81 |
|
Py thon_25_License. tx t |
101 |
6.83 |
6.83 |
6.87 |
|
Result_analysis.xls |
286 |
5.97 |
5.78 |
5.99 |
|
Metconv.txt |
1156 |
|||
|
Photo0139.jpg |
1272 |
6.45 |
6.44 |
6.45 |
|
Wildlife.wmv |
25631 |
4.94 |
4.92 |
4.93 |

FIGURE 7.5
Chi-Square values in logarithmic (base 10) scale.
Simulation-Based Results
In this section, the authors have tried to prove and conclude that this proposed cipher, RCC, is indeed a lightweight cryptography in view of its implementation. These analyses may be used to optimize the micro-architecture proposed. These analyses will also helpful for designing any lightweight system for IoT devices. The utilization summary is the list of all the hardware/GE components used in this design and numbers of each of these components used. From the results, it can be stated that this micro-architecture security solution is indeed applicable for IoT security.
Table 7.3 summarizes the synthesis report (Navabi, 2008; Wolf, 2009) which was obtained after successful implementation using IEEE VHDL through simulation in Xilinx ISE 8.1i (Wolf, 2009). The number of four-input Look-Up-Tables (LUTs) of RCC used is 53 and the
TABLE 7.3
Synthesis Summary of Proposed Micro-Architecture
|
Device Utilization Summary Logic Utilization |
Used |
Available |
Utilization |
|
Number of 4 input LUTs |
53 |
1,920 |
2% |
|
Logic Distribution |
|||
|
Number of occupied Slices |
27 |
960 |
2% |
|
Number of Slices containing only related logic |
27 |
27 |
100% |
|
Number of Slices containing unrelated logic |
0 |
27 |
0% |
|
Total Number of 4 input LUTs |
53 |
1,920 |
2% |
|
Number of bonded IOBs |
20 |
66 |
30% |
|
Total equivalent gate count for design |
324 |
||
|
Additional JTAG gate count for IOBs |
960 |
number available is 1920, so utilization is 2%. Number of occupied slices of RCC is 27 and available is 960, 2% is the utilization. The number of slices containing related logic of RCC is 100% and it is worth stating that this result is the same for other implementations also. The number of used slices with unrelated logic of RCC is 0%. The number of bonded input- output blocks (IOBs) of RCC is 20 out of 66, so utilization is 30%. The total equivalent gate count is only 324 and the additional JTAG gate count for IOBs is only 960. Therefore, it can be stated that the RCC is indeed a lightweight cryptography with respect to the available resources in Xilinx FPGA.
Applications
Some of the applications of the proposed RCC-SPN-CBC block cipher/micro-architecture are listed below:
- • The proposed cipher, RCC, is well suited for various embedded systems such as mobile phones, smart watches and IoT network devices as it is simple and easy to implement.
- • Electronic code books for encoding English alphabets are another application area.
- • Virtual Private Networks (known as VPN) and also master-key-based security protocols are both good application areas.
- • This technique, RCC, is suitable for hardware applications such as switches, gateways and routers.
Conclusion
Therefore we can conclude in this chapter that we have successfully proposed and implemented a lightweight cryptographic technique using RCC-SPN-CBC block cipher. The cryptanalysis test done with RSA and TDES using Chi-Square values generates better and also comparable results. Chi-Square based cryptanalysis is a widely used method to test the NULL hypothesis. We can also conclude that RCC is heterogeneous or non-homoge- neous in contrast to the widely used RSA and TDES. Moreover, simulation hardware-based results prove that the RCC is indeed a lightweight cryptography. The proposed cipher and micro-architecture can be used in various applications. The lightweight cryptography is widely used today to secure IoT and embedded devices. The RCC-SPN-CBC technique can also be used to develop encryption-based lightweight authentication protocols. The future scope of the author is to develop a lightweight hash function for message authentication and message integrity.
References
Bhasker, J. 2004. A VHDL Primer. Thirteen Indian Reprint 2004, Pearson Education Asia, Bengaluru, India, 14-82, ISBN: 81-7808-016-8 .
Chakraborty, R. and J. K. Mandal. 2006. "A microprocessor-based block cipher through rotational addition technique (RAT)/' in 9th International Conference on Information Technology (ICIT 2006), December 18-21, 2006, Bhubaneswar, India, 155-159, organized and sponsored by IEEE Computer Society, IEEE, ISBN-10: 0-7695-2635-7/06, ISBN-13: 978-0-7695-2635-5.
Chakraborty, R. and J. K. Mandal. 2011. "FPGA based cipher design & implementation of recursive oriented block arithmetic and substitution technique (ROBAST)," International Journal of Advanced Computer Science and Applications (IJACSA) 2(4), 54-59.
Chander, B. and K. Gopalakrishnan. 2020. "Chapter 21: Security Vulnerabilities and Issues of Traditional Wireless Sensors Networks in IoT," in Principles of Internet of Things (IoT) Ecosystem: Insight Paradigm, 519-549. Cham: Springer. DOI: https://doi.org/10.1007/978-3-030-33596-0_21.
Chatterjee, N. and J. K. Mandal. 2013. "Detection of blackhole behaviour using triangular encryption in NS2," in 1st International Conference on Computational Intelligence: Modeling, Technicjues and Applications (CIMTA-2013), Kalyani, India, 524-529, http://www.sciencedirect.com/science/ journal/22120173/10.
Colombier, B. and L. Bossuet. 2014. "Survey of hardware protection of design data for integrated circuits and intellectual properties," IET Computers & Digital Technicjues 8(6), 274—287. DOI: 10.1049/iet-cdt.2014.0028.
Dhanda, S. S., B. Singh, and P. Jindal. 2020. "Chapter 19: IoT Security: A Comprehensive View," in Principles of Internet of Things (IoT) Ecosystem: Insight Paradigm, 467-494. Cham: Springer. DOI: https://doi.org/10.1007/978-3-030-33596-0_19.
Forouzan, B. A. 2007. Cryptography and Network Security, Special Indian Edition 2007. Tata Mc-Graw- Hill India, 61-110: ISBN-13: 978-0-07-066046-5, ISBN-10: 0-07-066046-8.
Jha, P. K. and J. K. Mandal. 2011. Symmetric Encryption - Algorithm, Analysis and Applications. LAP - Lambert Academic Publishing, Latvia, European Union, 222-223, ISBN: 978-3-8454-2061-5.
Jha, S. K., N. Panigrahi, and A. Gupta. 2020. "Chapter 20: Security Threats for Time Synchronization Protocols in IoT," in Principles of Internet of Things (IoT) Ecosystem: Insight Paradigm, 495-517. Cham: Springer. DOI: https://doi.org/10.1007/978-3-030-33596-0_20.
Kaur, K. 2009. Digital System Design. Saarbriicken: Scitech Publications (India) Pvt. Ltd, 21-50, ISBN: 978-81-8371-188-3.
McKay, K. A., L. Bassham, M. S. Turan, and N. Mouha. 2017. "NISTIR 8114, Report on Lightweight Cryptography," 1-10. DOI: https://doi.org/10.6028/NIST.IR.8114.
Modersheim, S. and L. Vigano. 2019. "Alpha-beta privacy." ACM Transactions on Privacy and Security 22(1), 519-549, Article 7. DOI: https://doi.org/10.1145/3289255: .
Navabi, Z.. 2008. Embedded Core Design with FPGA(s), Edition 2008. New York: Tata Mc-Graw Hill India, 110-200. ISBN-13: 978-0-07-013978-7, ISBN-10: 0-07-013978-4.
Peng, S.-L., S. Pal, and L. Huang. 2020. Principles of Internet of Things (IoT) Ecosystem: Insight Paradigm, Intelligent Systems Reference Library, vol. 174. Cham: Springer, 467-549. DOI: https://doi. org/10.1007/978-3-030-33596-0.
Rupp, A., F. Baldimtsi, G. H. Lder, and C. Paar. 2015. "Cryptographic theory meets practice: Efficient and privacy-preserving payments for public transport," ACM Transactions on Information and System Security 17(3), 10:01-10:31, Article 10. DOI: http://dx.doi.org/10.1145/2699904.
Stallings, W. 2002. Cryptography and Network Security: Principle and Practice, 2nd edn. London: Pearson Education Asia, Sixth Indian Reprint, 6-90, ISBN: 81-7808-605-0.
Wolf, W. 2009. FPGA-Based System Design. London: Pearson Education Asia, First Impression - 2009, 121-448, ISBN: 978-81-317-2465-1.

